Manage Risk. Drive Confidence.
Strengthen your organization's governance framework, mitigate risks, and maintain regulatory compliance with expert GRC solutions. We help businesses build resilient operations, improve decision-making, and stay ahead of evolving regulatory requirements.
Our GRC Services
Veave Technologies delivers Governance, Risk & Compliance (GRC) services that help organizations strengthen governance, reduce risk exposure, and meet regulatory requirements.
Consulting
Our GRC consulting services help you build a strong foundation for organizational integrity and accountability. We assess your current GRC posture, identify gaps, and develop customized strategies aligned with your business goals and applicable frameworks like ISO 31000, NIST, GDPR, HIPAA, and more.
Key offerings include:
- Risk identification, analysis, and mitigation planning
- Alignment with industry-specific compliance frameworks and best practices
- Development and implementation of governance and internal control policies
- Data protection and privacy strategies tailored to applicable data laws
- Third-party and vendor risk management, including onboarding and continuous monitoring
- Business continuity and crisis management planning
We work closely with your team to implement pragmatic, scalable, and sustainable GRC strategies.
Training
Keeping your teams informed and equipped is crucial for successful GRC implementation. Our training services deliver hands-on, role-based learning experiences for executives, compliance officers, IT teams, and general employees.
We offer:
- In-house, virtual, and hybrid training sessions
- Certification-focused courses on ISO 27001, ISO 9001, GDPR, PCI DSS, NIST, HIPAA, and others
- Cyber hygiene awareness training to promote secure behavior across teams
- Specialized workshops on audit readiness, data privacy, incident response, and threat awareness
- Customized learning paths based on organizational roles and responsibilities
- Post-training assessments and certification of participation
Auditing
Regular audits are essential for identifying compliance gaps, operational risks, and inefficiencies. We offer independent, objective, and methodical auditing services to validate and strengthen your GRC programs.
Audit types include:
- Internal and external audit readiness assessments
- IT risk audits, controls testing, and support for cybersecurity assessments
- Regulatory compliance audits aligned with ISO standards, SOC 2, HIPAA, and PCI DSS
- Cybersecurity maturity evaluations and improvement planning
- Operational audits to identify inefficiencies and streamline compliance activities
- Custom audit checklists, findings reports, and post-audit support
Certification
Achieving recognized certifications demonstrates compliance and enhances brand credibility. We guide you throughout the certification lifecycle—from initial assessment to successful audit closure.
Certifications supported include:
- ISO 27001 – Information Security Management
- ISO 22301 – Business Continuity Management
- ISO 9001 – Quality Management
- SOC 2 – Trust Services Criteria
- PCI DSS – Payment Card Industry Compliance
Our team ensures you are well-prepared, documentation-ready, and aligned with certification bodies’ expectations.
Virtual CISO (vCISO)
Hiring a full-time CISO can be expensive and challenging. Our vCISO service offers access to senior-level cybersecurity leadership on a flexible basis.
What our vCISO provides:
- Strategic information security planning and policy development
- Implementation of security frameworks and compliance alignment
- Ongoing guidance on regulations such as GDPR, HIPAA, and CCPA
- Incident response planning and breach management coordination
- Executive and board-level reporting with actionable KPIs and metrics
- Security roadmap creation and maturity assessments for long-term improvement
Your dedicated vCISO acts as a trusted advisor, helping you navigate complex security challenges and compliance requirements while staying within budget.
Why Choose Our GRC Services
Our Governance, Risk & Compliance (GRC) services help organizations build strong governance, proactively manage risks, and achieve regulatory compliance while aligning security initiatives with business objectives.
Key reasons to choose our GRC services include:
- Framework-aligned approach based on ISO, NIST, GDPR, HIPAA, PCI DSS, and global best practices
- Practical and scalable GRC strategies tailored to your business size and industry
- Experienced consultants with deep expertise in governance, risk, and compliance
- End-to-end support covering consulting, training, auditing, certification, and vCISO services
- Audit-ready documentation and compliance evidence preparation
- Executive-level advisory to support informed decision-making and long-term resilience
GRC Solutions Across Multiple Industries
Our Governance, Risk & Compliance services support organizations across industries where regulatory compliance, risk management, and operational transparency are critical.
Banking & Financial Services
Helps financial institutions meet regulatory requirements and strengthen governance frameworks.
Healthcare & Life Sciences
Ensures secure patient data management and regulatory compliance.
IT, SaaS & Technology
Strengthens cybersecurity governance and compliance frameworks.
Manufacturing & Industrial
Improves operational resilience and risk management processes.
Telecommunications
Helps telecom providers manage cybersecurity and regulatory risks.
E-commerce & Digital Businesses
Strengthens payment security and customer data protection.
Our industry-focused approach ensures GRC strategies are aligned with sector-specific regulations and risk profiles.
How to Achieve GRC Certification
Achieving certifications such as ISO 27001, SOC 2, PCI DSS, and ISO 22301 requires a structured process. Our GRC experts guide organizations through every stage of the certification journey to ensure compliance, audit readiness, and successful certification.
Step 1 – Gap Assessment
Evaluate your current security posture and identify compliance gaps against required certification frameworks.
Step 2 – Implement Controls
Develop policies, procedures, and security controls aligned with certification requirements.
Step 3 – Risk Assessment
Identify potential risks and implement mitigation strategies to strengthen security and governance processes.
Step 4 – Internal Audit
Conduct internal audits to ensure your organization is fully prepared for the certification assessment.
Step 5 – Certification Audit
Work with an accredited certification body to complete the audit and obtain your compliance certification.
Frequently Asked Questions
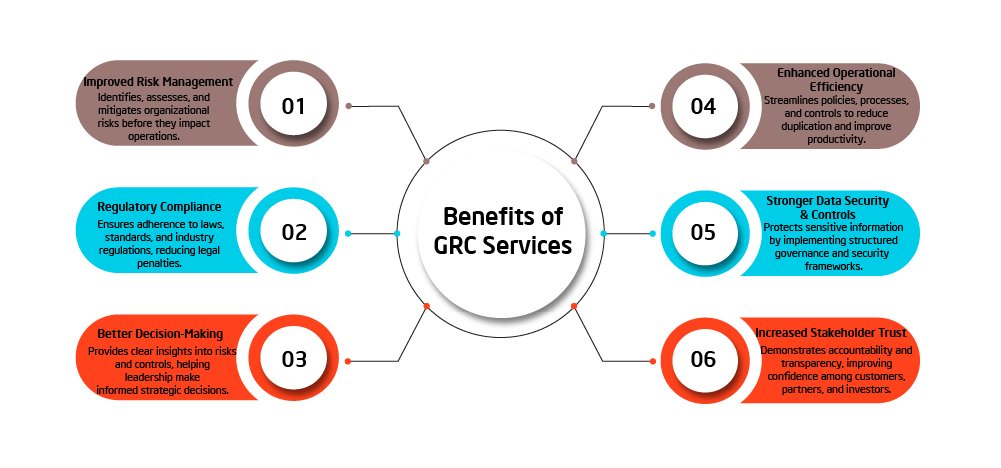
Governance, Risk, and Compliance (GRC) is a structured approach that helps organizations manage governance policies, identify risks, and ensure compliance with regulatory requirements. At Veave Technologies, our GRC services help businesses build strong governance frameworks while improving operational transparency and regulatory compliance.
GRC helps organizations identify risks, meet regulatory requirements, and implement strong governance practices. Veave Technologies supports businesses with effective GRC strategies that strengthen security, protect sensitive data, and improve stakeholder trust.
Veave Technologies provides comprehensive GRC services including consulting, training, auditing, certification support, and Virtual CISO (vCISO) services to help organizations manage risks and maintain compliance.
Our GRC consulting services align with global frameworks such as ISO 27001, ISO 31000, NIST, GDPR, HIPAA, SOC 2, and PCI DSS to ensure strong risk management and regulatory compliance.
A Virtual Chief Information Security Officer (vCISO) is an outsourced cybersecurity leadership role. Veave Technologies provides vCISO services that guide organizations in implementing security strategies, managing risks, and maintaining compliance.
GRC audits identify compliance gaps, evaluate internal controls, and strengthen risk management processes. Veave Technologies provides detailed audit reports and improvement recommendations to help businesses meet regulatory standards.
Organizations can achieve certifications such as ISO 27001, ISO 9001, ISO 22301, SOC 2, and PCI DSS with the support of Veave Technologies’ GRC services.
GRC training helps employees understand compliance policies, risk management practices, and cybersecurity awareness. Veave Technologies provides role-based training programs to strengthen organizational security culture.
Industries such as banking, healthcare, IT & SaaS, manufacturing, telecommunications, e-commerce, and government sectors benefit from strong GRC frameworks to manage regulatory compliance and risks.
You can contact Veave Technologies for a consultation or GRC assessment. Our experts will evaluate your current governance, risk, and compliance posture and create a customized roadmap to improve security and regulatory readiness.